For CISOs
Give teams room to adopt AI, with clear oversight.
Review reported skills and AI connections, manage model rules, and inspect the records behind AI activity.
“AI tools moved faster than our policies. Tokenize shows us which models and MCP servers people are actually using, so we catch what shouldn't be there before it becomes a problem.”
MCP Governance
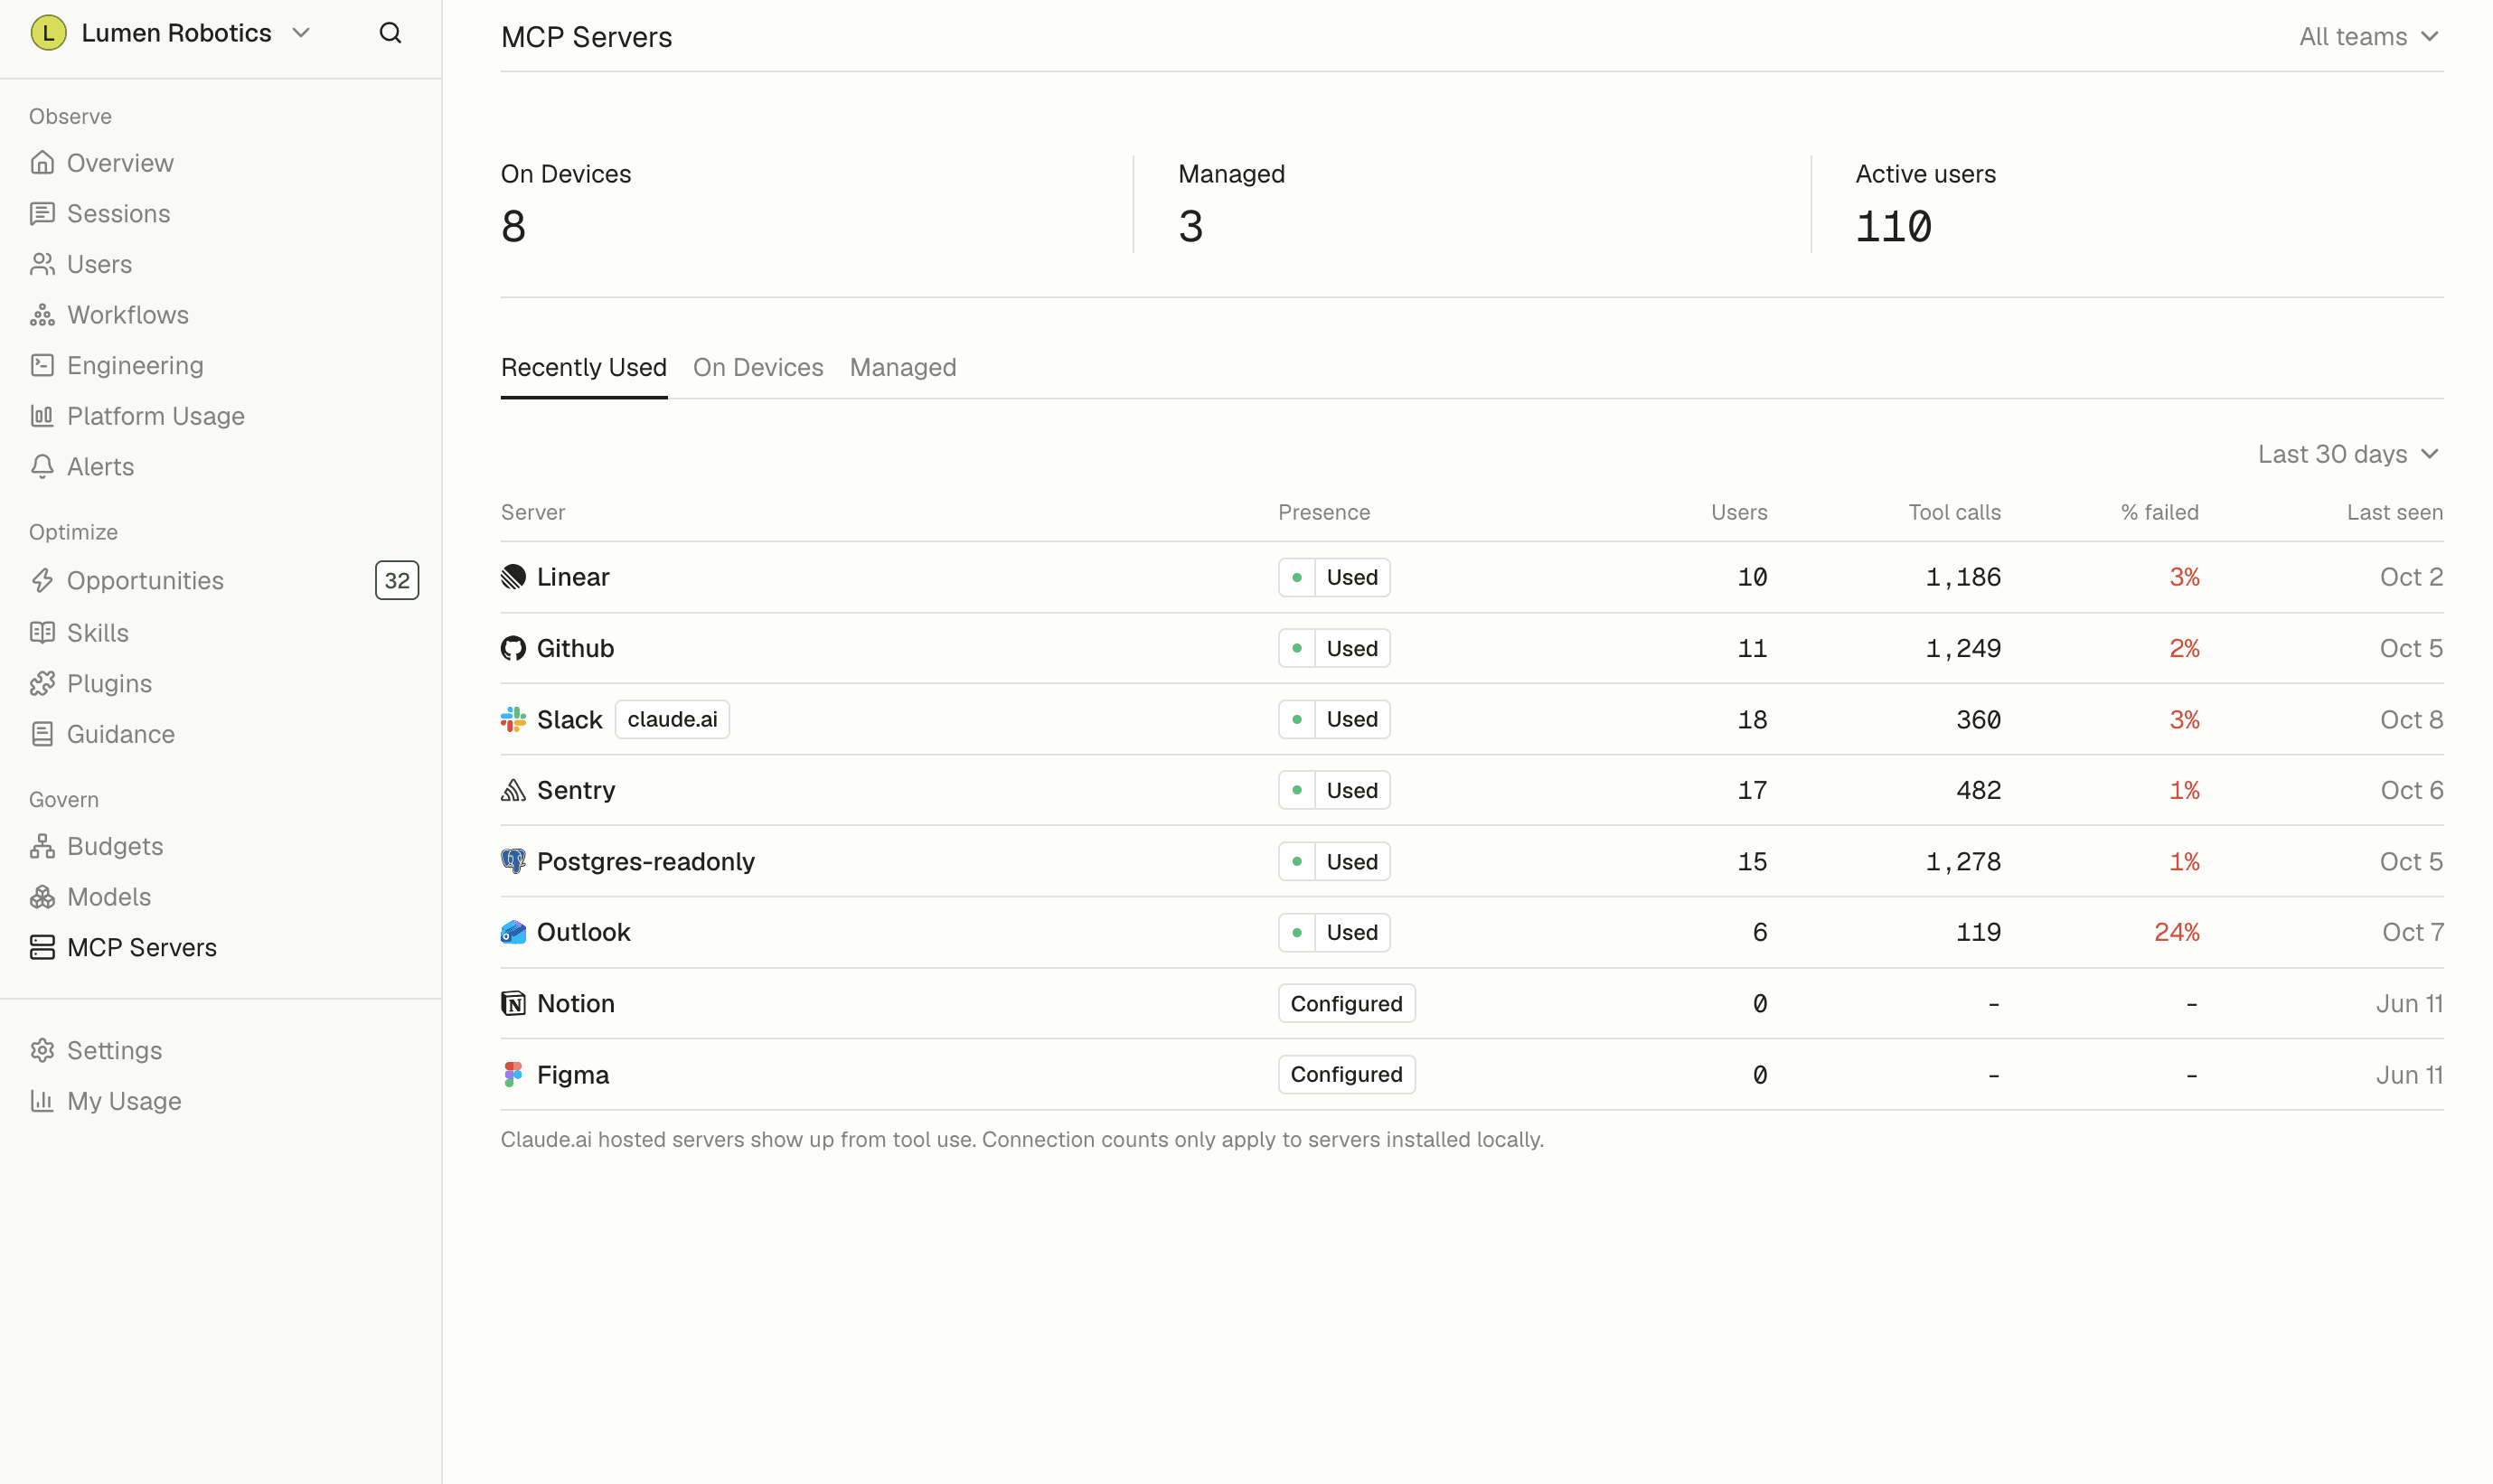
Know what people add to their AI tools.
Review reported skill usage and MCP servers on enrolled devices. Inspect captured Codex skill files to support your security reviews.
AI Model Control
Manage models, skills, and connections.
Set allowed-model rules for Claude Code and Codex on enrolled devices. Deploy the managed skills and MCP configurations your organization chooses to selected teams.
AI Spend Observability
Make AI use easier to review.
Inspect recorded sessions, model usage, tool calls, and guidance change history to support internal reviews. Choose how much session content Tokenize collects and who can access it.
Key features for CISOs
Skills and MCP inventory
Review reported skill usage and MCP activity on enrolled devices, plus captured Codex skill files where available.
Learn more →AI Model Control
Set default and allowed models for Claude Code and Codex on enrolled devices.
Learn more →Managed skills and connections
Publish managed skills to Claude Code and Codex, and managed MCP configurations to selected enrolled devices. Check reported delivery status.
Learn more →Usage records and guidance history
Review captured AI activity and the versions, authors, and dates of published guidance changes.
Learn more →Data collection controls and permissions
Configure prompt and full-session-content collection on enrolled devices, and restrict access through application permissions. Both content settings are enabled by default.
Learn more →
Frequently asked questions
See all FAQsWhat data does Tokenize collect?
Records of AI assistant work: which tool and model ran, when, how many tokens, what it cost, and what kind of task it was. Whether prompt text is included is your organization's choice, and it is a setting you control.
What is redacted?
Secrets such as passwords and API keys are removed before data leaves the device, so Tokenize never stores the original values.
Can we turn off prompt content entirely?
Yes. An organization-level setting prevents prompt text from being sent. Cost, token, and usage data remain available when prompt content is off.
Where does the data go?
To Tokenize's own hosted pipeline, over an encrypted connection, authenticated with a key issued to your organization.
Who inside my company can see what?
Access follows the roles you set. Admins see the organization-wide view, individuals see their own. Directory sync keeps that accurate without manual cleanup.
Do you have a SOC 2 report?
Our latest security and compliance documentation, including our current SOC 2 status and available reports, lives in the Tokenize Trust Center. You can review the public materials there or request access to restricted documents.
- GDPR
- SOC 2 Type II
- SAML SSO
- SCIM Provisioning